
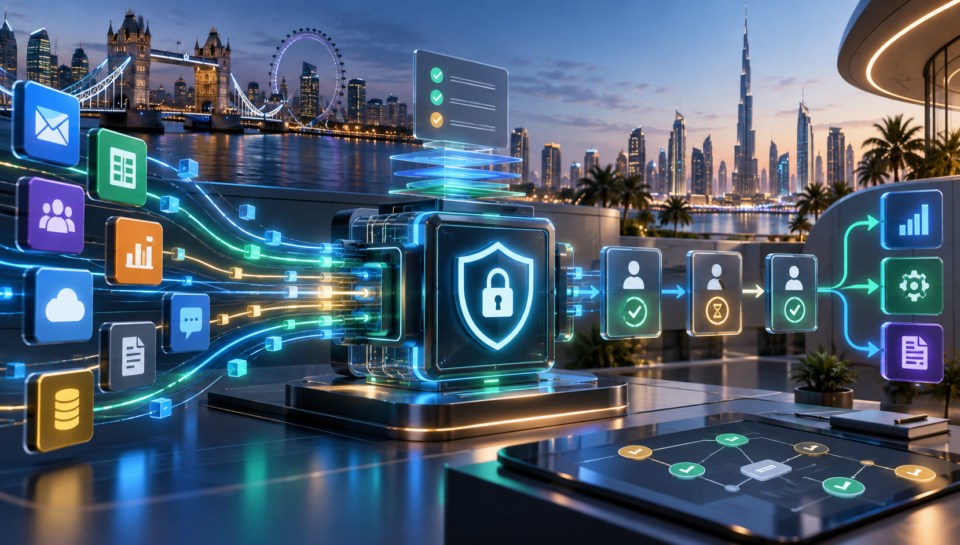
Secure no-code integration governance is what turns a collection of convenient automations into a dependable business system. When forms, CRM records, email platforms, finance tools, cloud storage and AI services exchange data automatically, every connection becomes both a productivity gain and a point that needs ownership.
This guide gives UK and UAE SMEs a practical governance model for no-code and low-code integrations without slowing useful innovation.
Why integration governance matters
No-code tools make it easy to connect systems in hours rather than months. The risk is that workflows can spread faster than documentation, access reviews and recovery plans. A departed employee may still own a connector, an API token may have broader permissions than necessary, or a silent error may stop leads reaching the CRM.
Good governance is not a ban on automation. It is a lightweight operating system that makes each workflow visible, proportionate, testable and recoverable.
The seven controls every automated workflow needs
1. A named business owner
Assign one person who understands the outcome the workflow supports, such as lead follow-up, invoice processing or customer onboarding. The owner approves changes, reviews failures and confirms that the automation still serves a real need.
2. A simple integration register
Record the trigger, connected apps, data fields, account owner, credentials location, vendor, business purpose, retention needs and last review date. A shared spreadsheet is enough to start. The objective is visibility, not paperwork.
3. Least-privilege access
Give each connection only the permissions it requires. A workflow that adds a lead to a CRM should not automatically receive permission to delete all records. Use dedicated service accounts where appropriate, enable multi-factor authentication and review access after staff or supplier changes.
4. Data minimisation and clear purpose
Move only the fields needed for the stated outcome. The UK ICO’s data-protection-by-design guidance recommends integrating safeguards from the earliest design stage and throughout the lifecycle. UAE organisations should also map applicable federal, free-zone and sector rules before transferring personal data between services or regions.
5. Human approval at consequential steps
Low-risk actions such as tagging a record may run automatically. High-impact steps—sending a contract, changing financial data, deleting information or publishing externally—should have an appropriate review or approval gate. See our human-in-the-loop document automation workflow for a practical model.
6. Monitoring, alerts and audit trails
Track successful runs, failures, retries and unusual volumes. Send alerts to a shared operational channel rather than one person’s inbox. Retain enough evidence to investigate what happened without storing unnecessary personal data.
7. A tested off-switch and recovery plan
Document how to pause the automation, revoke credentials, replay failed items and return to a manual process. Test recovery before a workflow becomes business-critical. Backups matter only if the team knows how to restore service.
A practical risk-rating method
Score each workflow across four questions: how sensitive is the data, how many records are affected, how consequential is the automated action and how quickly could the team detect a failure? A simple low, medium or high rating determines the review frequency.
- Low risk: internal reminders or non-sensitive record tagging; review every six months.
- Medium risk: lead routing, email sequences or customer data syncing; review quarterly.
- High risk: payments, contracts, identity data, deletion or public publishing; review monthly and require human approval.
UK and UAE considerations
For UK operations, data protection by design should be embedded before processing begins, not added after launch. Document the lawful basis, data flows, processors and retention logic. For online services, the UK National Cyber Security Centre recommends secure configuration, strong authentication and preparation for losing access to a critical cloud service.
For UAE teams, identify which legal regime and regulator apply to the organisation and data. Consider where vendors host and process information, whether cross-border transfers are involved and whether Arabic-language notices or customer support are needed. Multi-market teams should keep one master integration register with market-specific compliance notes.
A 10-step rollout checklist
- Choose one repetitive, measurable business process.
- Map the current manual steps and exceptions.
- Name the business owner and technical maintainer.
- List every app, field and user role involved.
- Remove unnecessary data and permissions.
- Add validation, duplicate checks and approval gates.
- Test normal, missing-data and failure scenarios.
- Configure alerts and a shared audit trail.
- Document pause, rollback and manual fallback steps.
- Review outcomes after 30 days and adjust the risk rating.
How to choose a no-code platform responsibly
Evaluate security controls, data residency options, role management, logging, export capability, service limits and incident communication. Check whether the platform can support separate development and production workflows and whether credentials can be rotated without rebuilding everything.
Cost should include monitoring and maintenance, not just monthly licence fees. A cheaper connector that fails silently can be expensive when enquiries, orders or compliance evidence go missing.
Frequently asked questions
Is no-code automation secure?
It can be, when access is limited, data flows are understood, vendors are assessed and workflows are monitored. The platform does not remove the organisation’s responsibility for configuration and oversight.
Who should own an integration?
A business owner should be accountable for the outcome, while a technical maintainer manages configuration. Avoid workflows owned only by an individual employee’s personal account.
How often should automations be reviewed?
Review frequency should follow risk. High-impact workflows deserve monthly checks; medium-risk workflows quarterly; simple low-risk workflows at least every six months and after any system or staffing change.
Should AI steps be treated differently?
Yes when an AI model interprets unstructured content or recommends consequential actions. Add confidence thresholds, human review, restricted tool access and output monitoring. Our AI agent governance checklist covers these controls in more detail.
Build automation your team can trust
Secure no-code integration governance creates speed with accountability. Creative & Co. helps UK and UAE businesses design CRM, website, chatbot and app workflows that are documented, measurable and maintainable.
Need a dependable automation roadmap? Talk to Creative & Co. about auditing existing integrations or building a governed workflow from the ground up.